The same disciplines. Different risk in every industry.
We adapt cyber security and compliance to each sector's data, services, dependencies, and regulatory pressure without turning every industry into the same IT package with a different name.
Choose the operating context closest to yours
Each sector keeps the same ZebraByte security and compliance disciplines while changing priorities, operating risks, and service mix.
We protect correspondence, confidential documents, the firm's website and infrastructure without turning legal activity into a permanent IT project.
Protection for sensitive data, accounts, forms, communication and infrastructure, with recovery and privacy integrated into the operating mode.
A common program for exposed public services, email, infrastructure, NIS2 readiness, GDPR and digital accessibility.
We protect checkout, accounts, email, and infrastructure without sacrificing store performance or availability.
Protection for forms, leads, emails, media-rich websites, and integrations used in the sales flow.
Protection for reservations, website, email, accounts and suppliers, with a focus on availability and rapid recovery.
We protect identities, operational applications, email, suppliers, and the continuity of technology-dependent processes.
We protect student platforms, accounts, and data, integrating security with GDPR and the accessibility of digital services.
A realistic baseline for email, website, data, SaaS, and recovery, suitable for small teams and distributed infrastructure.
One operating model, adapted to the sector
The sequence stays coherent. The scope, evidence, and technical emphasis change with the business context.
Map assets, data, suppliers, exposure, and obligations that actually change the risk.
Apply identity, hardening, website, email, and infrastructure controls where they matter.
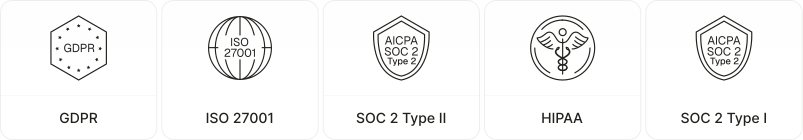
Connect technical controls to GDPR, NIS2, ISO 27001, SOC 2, or the relevant governance model.
Keep evidence, reviews, incidents, and remediation moving as systems and suppliers change.
Capabilities combine around the real risk
Some organizations need a focused assessment. Others need technical controls, compliance, and continuous operational ownership in the same program.
Managed Compliance
Controls, risk, evidence, privacy, and audit readiness in a continuously operated program.
Cyber Security
Assessment, identity, website/email security, hardening, and incident response aligned to real technical risk.
Regulatory readiness
GDPR, NIS2, ISO 27001, and other obligations connected to demonstrable processes and controls.
Penetration Testing
Authorized testing for applications, APIs, and infrastructure with verifiable findings and retesting.
Incident readiness
Response, recovery, and evidence prepared before a real incident forces the decision.
Don't see your industry?
We start with your data, applications, suppliers, and risk. You do not need to fit into a predefined category to begin.
Describe your contextDescoperă ce mai poate face ZebraByte
-
Serviciu Compliance Officer
Managed compliance de experți, cap-coadă
-
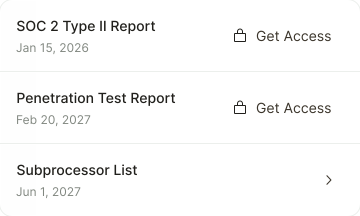
Compliance Portal
Partajează documente de securitate în siguranță
-
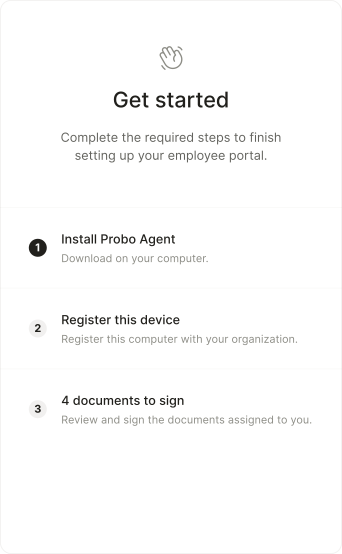
Employee Portal
Conformitatea întregii echipe, într-un singur portal
-
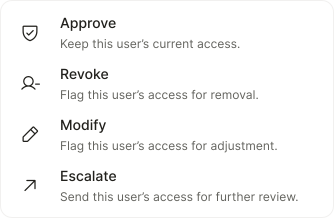
Access Review
Revizuiește accesul utilizatorilor în toate sistemele
-
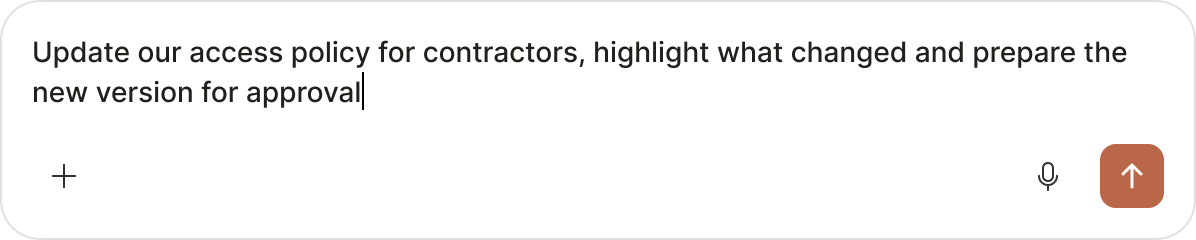
AI Agents
Rulează compliance din instrumentele pe care le folosești
-
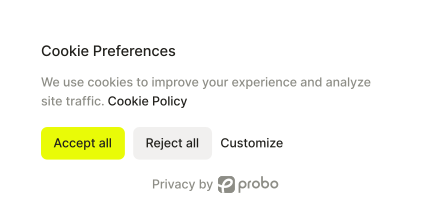
Cookie Banner
Consimțământ adaptat legislației fiecărui vizitator
-
Device Agent
Monitorizează continuu postura de securitate a dispozitivelor