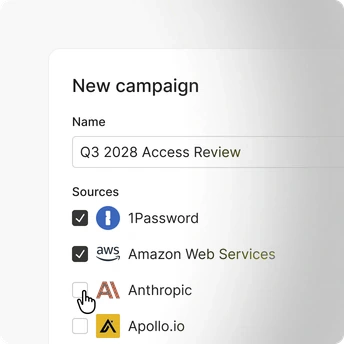
Campaigns
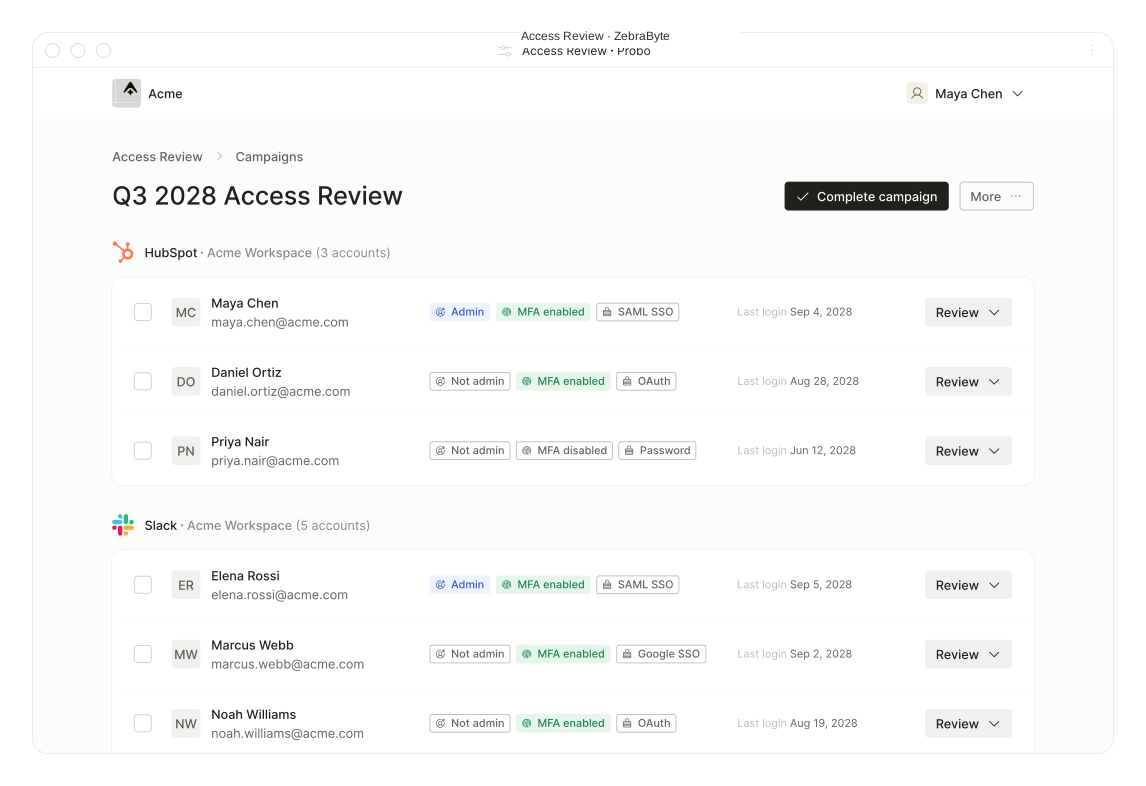
Scope a review to the systems that matter, then snapshot them in one click.

ZebraByte service access
Choose the service you want to manage.
Bring accounts from across your tools into one review. Spot risky access, make informed decisions, and keep a clear record for your next audit.
Book a demoConnect your tools
 1Password
 Amazon Web Services
 Anthropic
 Apollo.io
 authentik
 Azure
 Better Stack
 Brevo
 Brex
 Cal.com
 Calendly
 ClickHouse Cloud
 Cloudflare
 Crisp
 Cursor
 Deepgram
 Dotfile
 GitHub
 Google Cloud
 Grafana
 HubSpot
 incident.io
 Langfuse
 Mercury
 Metabase
 Neon
 Nuki
 Okta
 OpenAI
 OpenRouter
 Pylon
 Qovery
 Railway
 Render
 Resend
 Scaleway
 Segment
 SendGrid
 SigNoz
 Supabase
 Tailscale
 Tally
 UpCloud
 Yousign
Certify access across your stack in one workflow, with every decision preserved as point-in-time audit evidence.
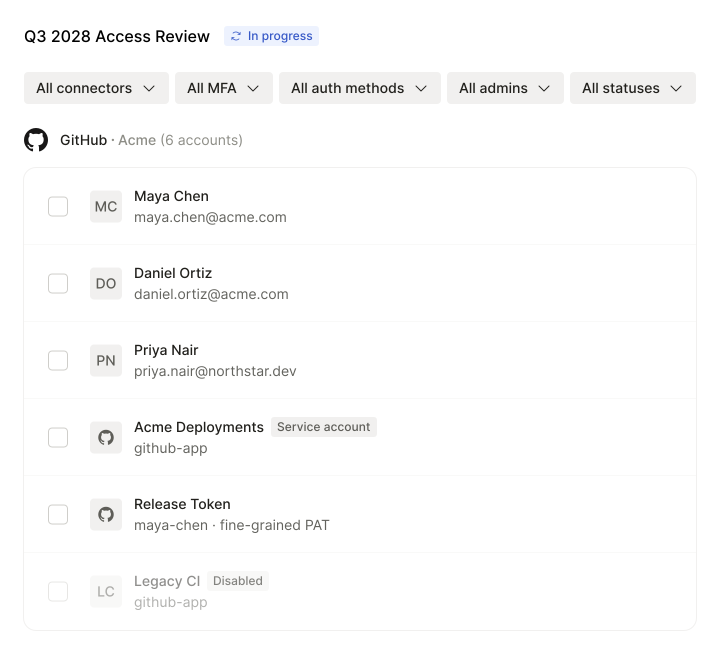
Bring accounts from Google Workspace, Okta, GitHub, cloud infrastructure, Slack, and Brex into one review.
Freeze who had access to what when the campaign starts, regardless of later changes.
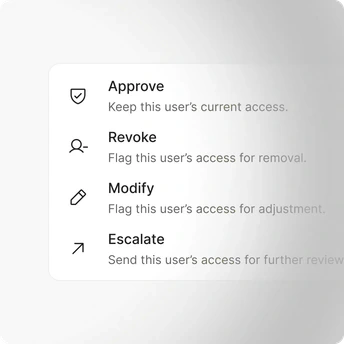
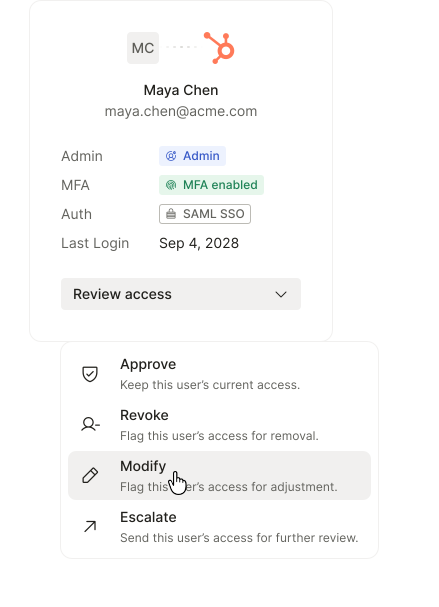
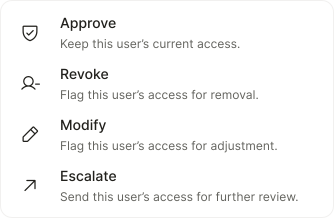
Approve, revoke, defer, or escalate, individually or in bulk. Notes are required except for approvals.
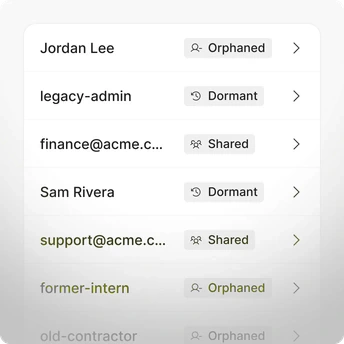
ZebraByte flags orphaned, dormant, over-privileged, and shared accounts for priority review.
Each campaign tags accounts as new, removed, or unchanged since the last.
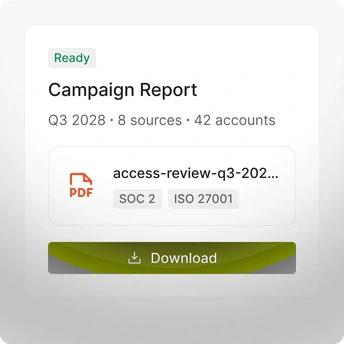
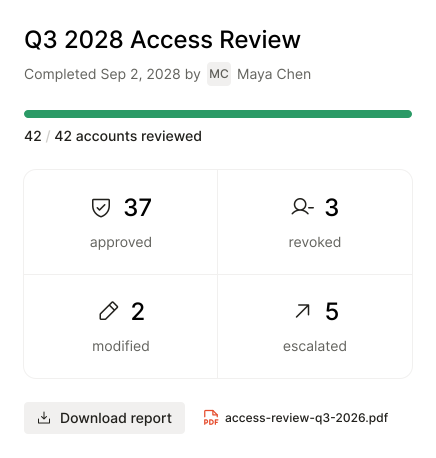
Export a closed campaign as a PDF recording who reviewed what, and why.
Connect every system once, capture the full picture, move through decisions fast, and close with proof auditors accept.
Sources, campaigns, access entries, flags, decisions, and statistics keep every review moving.
Scope a review to the systems that matter, then snapshot them in one click.
Connect providers and reuse them across campaigns.
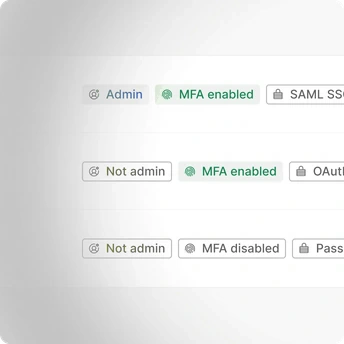
Every account with role, admin, MFA, and last login context to decide fast.
Orphaned, dormant, over-privileged, and shared accounts surfaced automatically.
Approve, revoke, defer, or escalate, with justifications kept on record.
Live counts by decision and flag, plus a PDF record auditors accept.
On working with the ZebraByte team.
“An excellent collaboration with a team I appreciated greatly. I recommend the experience of working with ZebraByte.”
Featured brands
You can connect identity, cloud, source code, SaaS and finance providers, and import CSV files for other systems.
Import a CSV export and review it alongside connected sources. Replace the CSV before the next campaign to obtain an updated snapshot.
Yes. ZebraByte can distinguish service accounts from people when the source identifies them, so non-human credentials can be assessed in the same campaign.
Yes. Select multiple accounts and apply decisions or flags in bulk. Actions with an impact retain their justification in the review.
A campaign is a snapshot at a specific point in time. Provider data may continue to change, but the accounts, context and decisions in the review are preserved.
It preserves records of who had access, reviewers' decisions and their justifications. The record can support access review controls for a SOC 2 or ISO 27001 audit.
Complete the campaign once every account has a decision, then export the review as a PDF for the auditor.
Quarterly is a common cadence, with additional campaigns after significant changes to roles, systems or the organization. The final frequency should align with your policy and the auditor's requirements.
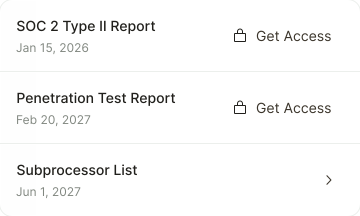
Share security documents securely
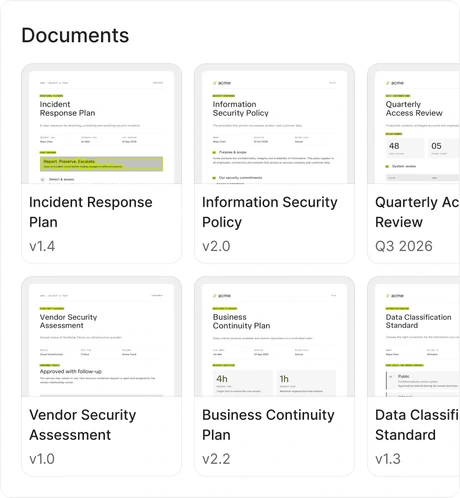
Draft, approve, and sign your policies
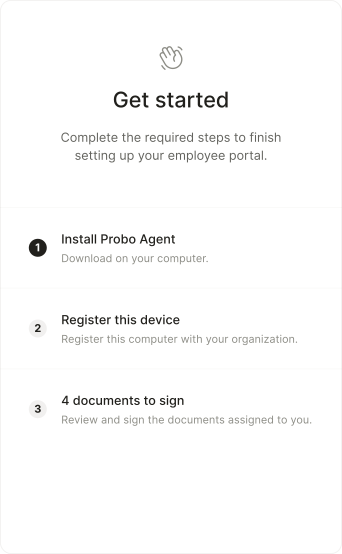
Your whole team’s compliance, in one portal
Monitor user access across all your systems
Run compliance from the tools you use
Consent that follows every visitor's law
Monitor device security posture continuously