
FRAMEWORKS / READINESS / Security
SOC 2 Type II
Assessment of control design and operating effectiveness over an examination period.

SCOPE & APPLICABILITY
What the framework actually requires
Independent assurance reporting across a specified examination period.
What matters in practice
Requirements depend on scope. These are the areas to evaluate, not a guarantee of certification or regulatory compliance.
Period and scope
Establish controls and ownership.
Recurring evidence
Collect evidence throughout the period.
Exceptions and remediation
Track exceptions and prepare for examination.
An operational path, not a checkbox exercise
Translate requirements into accountable activities, evidence and reviewed controls.
Establish controls and ownership.
Collect evidence throughout the period.
Track exceptions and prepare for examination.
APPLICABILITY
Who should assess this framework?
For service organisations needing to demonstrate that controls actually operate consistently throughout an examination period rather than merely being documented.
BEYOND CHECKLISTS
Why this matters
Type II demands operational discipline across monitoring, access, onboarding/offboarding, change management and evidence retained throughout the period.
EVIDENCE & OPERATIONS
What your organisation should be able to evidence
This is a practical starting point, not an exhaustive set of regulatory obligations or a substitute for an independent audit.
- 01 System description and examination period
- 02 Control ownership and execution frequencies
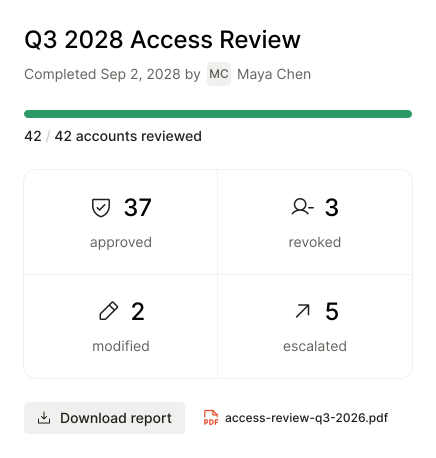
- 03 Access reviews and offboarding records
- 04 Change management and incident response evidence
- 05 Exceptions, periodic tests and tracked remediation
- 06 Provider due diligence and monitoring records
FAQ
Frequently asked questions
Practical distinctions worth understanding before starting your programme.
How long must a Type II examination period be?
It depends on the examination objectives and agreement with the independent auditor. No single period fits every organisation.
Can controls also support ISO 27001?
Some controls and evidence can be mapped, but criteria, scope and audit outcomes are different.
Can software issue a SOC 2 report?
No. The independent auditor issues an attestation report following examination.
FURTHER READING
Explore related resources
Use original ZebraByte articles and guides to explore security programmes, privacy governance and readiness.
Framework descriptions are educational. Applicability, service availability and any independent assessment require confirmation for your organisation.
Important scope boundary
ZebraByte can discuss readiness, technical controls and programme management. A regulator, qualified auditor or certification body makes the applicable independent determination. Support for a particular framework is subject to the agreed service scope.
Related frameworks and programmes
Need a scope assessment for your organisation?
Share your sector, systems and contractual requirements. We can outline the next practical steps and clarify whether this framework is relevant.