
Turn Your SOC 2 into a Trust Asset
Communication Guidelines
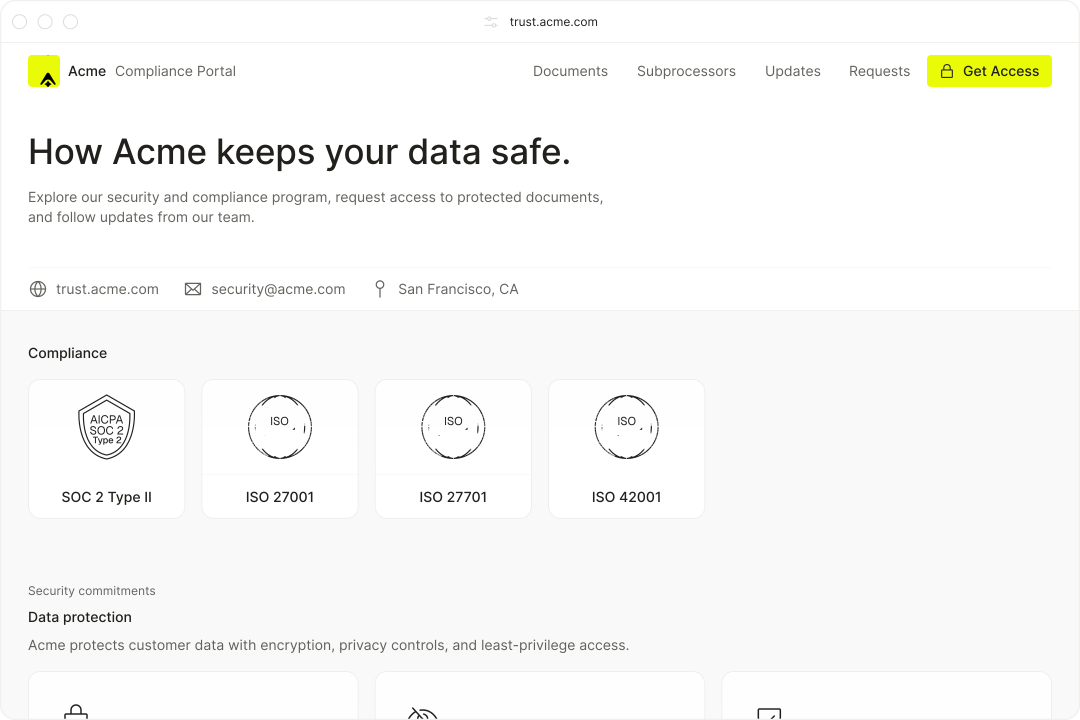
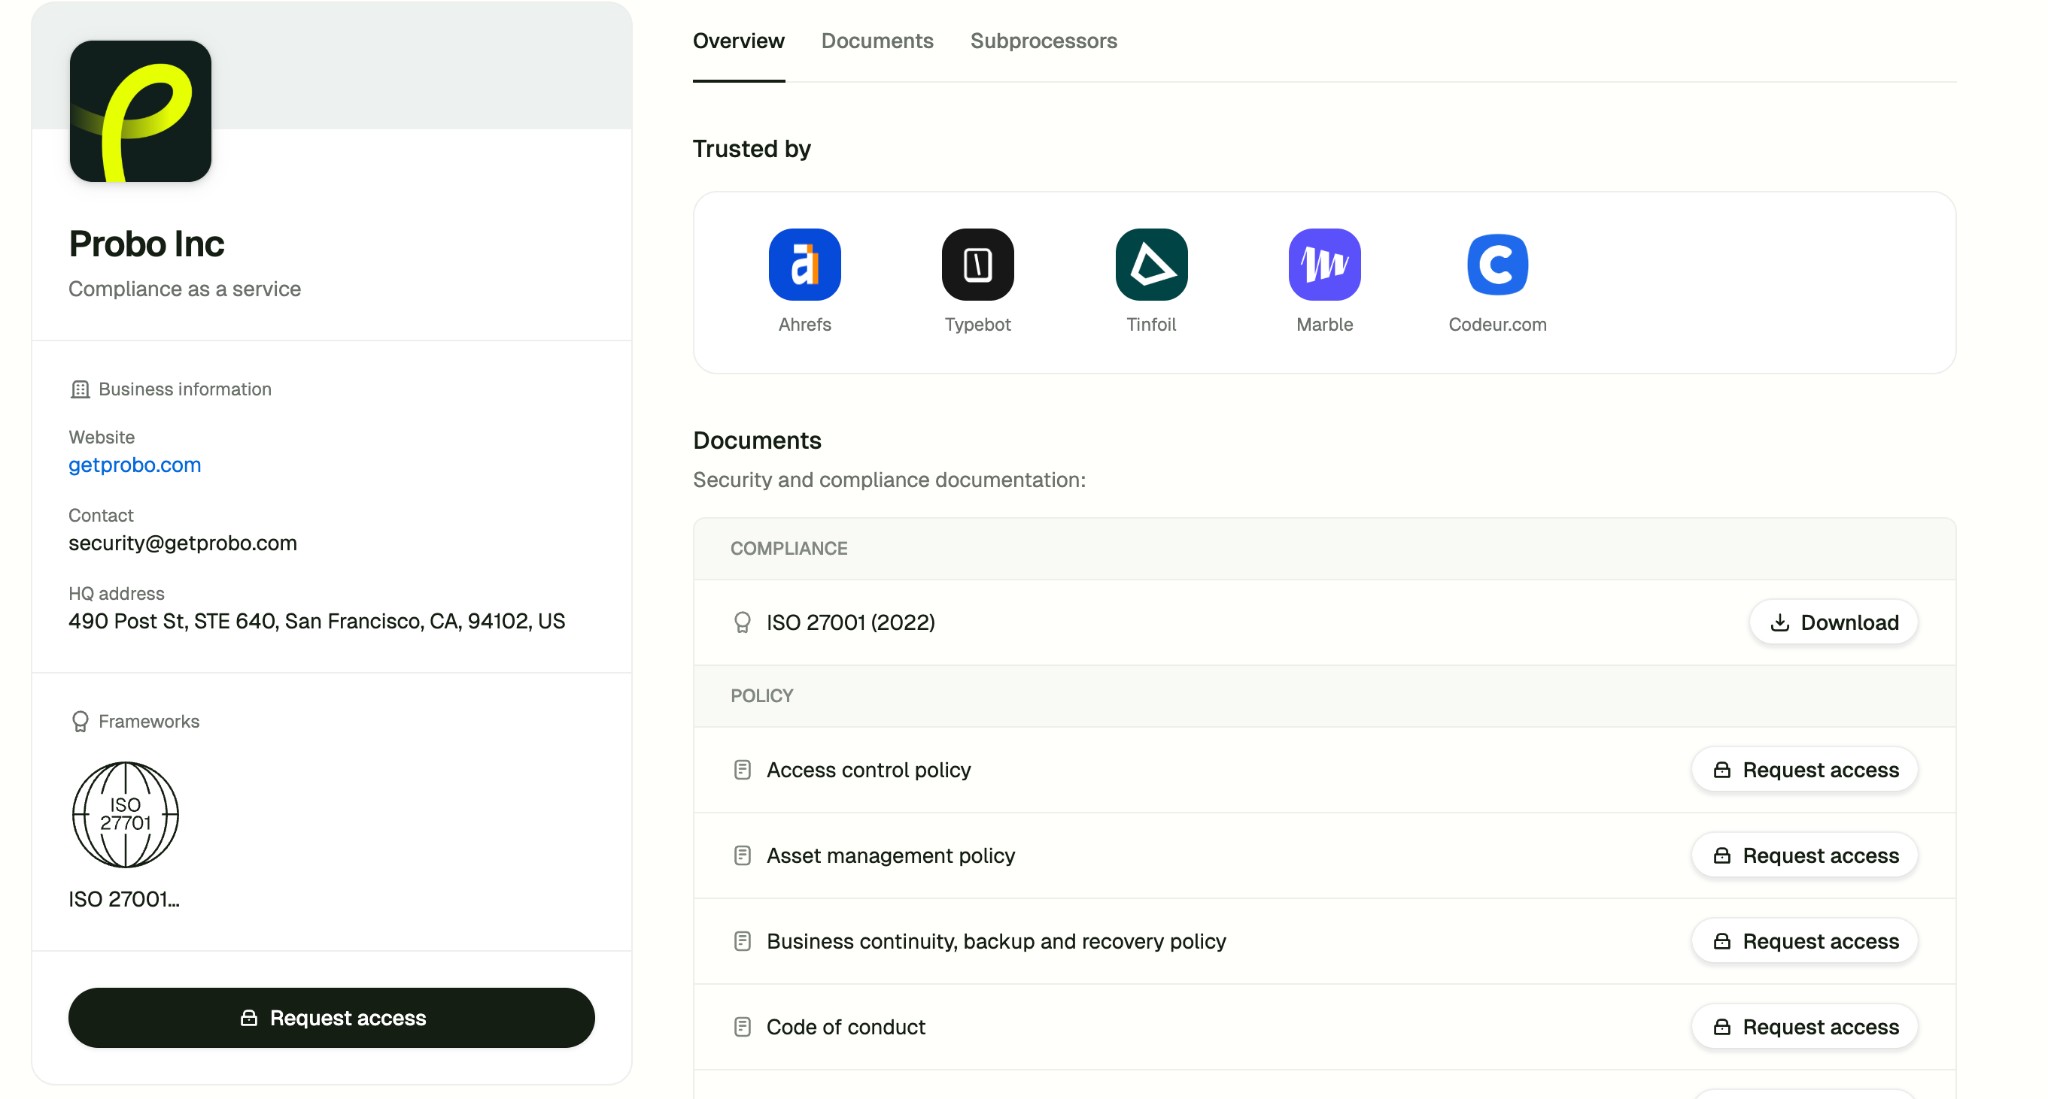
Trust center
Create or update your Trust Center to showcase your new SOC 2 report.
You don't have a Trust Center yet?
Reach out to the ZebraByte team, we will get yours for free.
Example
Achievement
Value for Customers
Access to the Report
Linkedin post & blog article content
Linkedin post
It is now a good time to inform your customers and prospects about your new milestone.
We recommend you to start by posting it on your Linkedin page (if you tag ZebraByte we will be glad to share it).
Here is an example you can use:
Big announcement: [COMPANY NAME] is now SOC 2 Compliant! 🔒
I'm excited to share that [COMPANY NAME] has officially achieved SOC 2 compliance, an important step in our commitment to the highest standards of security, reliability, and trust for our customers.
A big thank you to @ZebraByte, whose platform and team made the entire SOC 2 journey significantly smoother.
What this means for our customers:
- Increased trust and transparency
- Stronger data protection
- Enterprise-ready infrastructure
Proud of what the team has accomplished, and excited for what this unlocks next.
Linkedin asset template
You can download and customize this template to visually support your post, if needed.

Blog article
It is a good practice to create a page about your SOC 2 report to give
context to your customers and prospects.
You can also link this page to the SOC 2 logo display on your
website.
✏️
[Company Name] Achieves SOC 2 Compliance, Reinforcing Its Commitment to Security and Trust
We're proud to announce that [Company Name] is now SOC 2 compliant, marking a major milestone in our ongoing commitment to security, reliability, and transparency for our customers and partners.
This milestone was achieved in close partnership with ZebraByte, who led our compliance process.
What this means for our customers
SOC 2 compliance provides independent assurance that [Company Name] operates with strong internal controls designed to protect customer data.
For our customers, this means:
- Increased confidence in how we protect sensitive information
- Reduced vendor risk and easier security reviews
- Alignment with enterprise, regulatory, and procurement requirements
- Proof that security is embedded in our day-to-day operations, not just promised
SOC 2 is not a one-time checkbox. It represents a continuous commitment to maintaining high standards across our organization.
What is SOC 2, exactly?
SOC 2 is a widely recognized compliance framework developed by the American Institute of Certified Public Accountants (AICPA).
For [Company Name], the SOC 2 examination focused on the Trust Services Criteria most relevant to how we build and operate our product:
[Keep only Trust Services Criteria on report]
- Security – Protection against unauthorized access
- Availability – System reliability and uptime
- Confidentiality – Safeguarding sensitive information
- Processing Integrity – Accuracy and completeness of system processing
- Privacy – Proper handling of personal data
An independent auditor validated that these controls operated effectively over an extended period ([XX/XX/XXX to XX/XX/XXX]), providing assurance that our security practices are consistently enforced day to day.
Thanks to ZebraByte's structured approach and hands-on guidance, we were able to move through the compliance process faster, with clarity, and without disrupting our core operations.
How to access our SOC 2 Report
The full SOC 2 Type II report is a restricted-use document and is available to customers and prospective customers under NDA upon request.
[To adapt depending on process]
To request access:
- Contact your [Company Name] sales or account representative, or
- Reach out to us via [contact link or email]
Assets for your website
Compliance Badges for SOC 2


Rule to display the official AICPA SOC logo
If you want to display the official AICPA SOC logo on your website, you have to register first.
The report and the trademark are two separate things, and the AICPA has been enforcing this more actively since April 2026.
Registration takes five minutes. You'll need the name and license number of the CPA who signed your report, and the report date.
Register directly on the AICPA & CIMA website (free account required) or ping us to handle it for you.
One more thing: the logo expires. If 12 months pass without a new report, you have to take it down.
ZebraByte logo
Add the ZebraByte logo next to your compliance badge to highlight your certified status.


Turn compliance into business growth
Turn SOC 2 into a sales accelerator
Proactively mention SOC 2 early in sales conversations or outbound messages.
"We're SOC 2 Type II audited, covering security, availability, and confidentiality."
Replace long security questionnaires: offer to share SOC 2 report under NDA.
This can cut weeks off enterprise deals.
Make your compliance a competitive advantage
If competitors are not SOC 2: mention it explicitly in competitive deals.
Website placement
Add SOC 2 (small badge or text) signals in:
- Website placement
- Footer
- Security / Trust page
- Pricing or Enterprise page
- Signup pages
Example

Inform & train your team (sales and CS)
Share with them the guideline and blog article document.
Make sure they can confidently answer:
Strengthen customer retention & expansion
Announce SOC 2 to existing customers:
- Customer newsletter
- In-app notification
Position it as:
"An investment we made to protect you as you scale with us."