
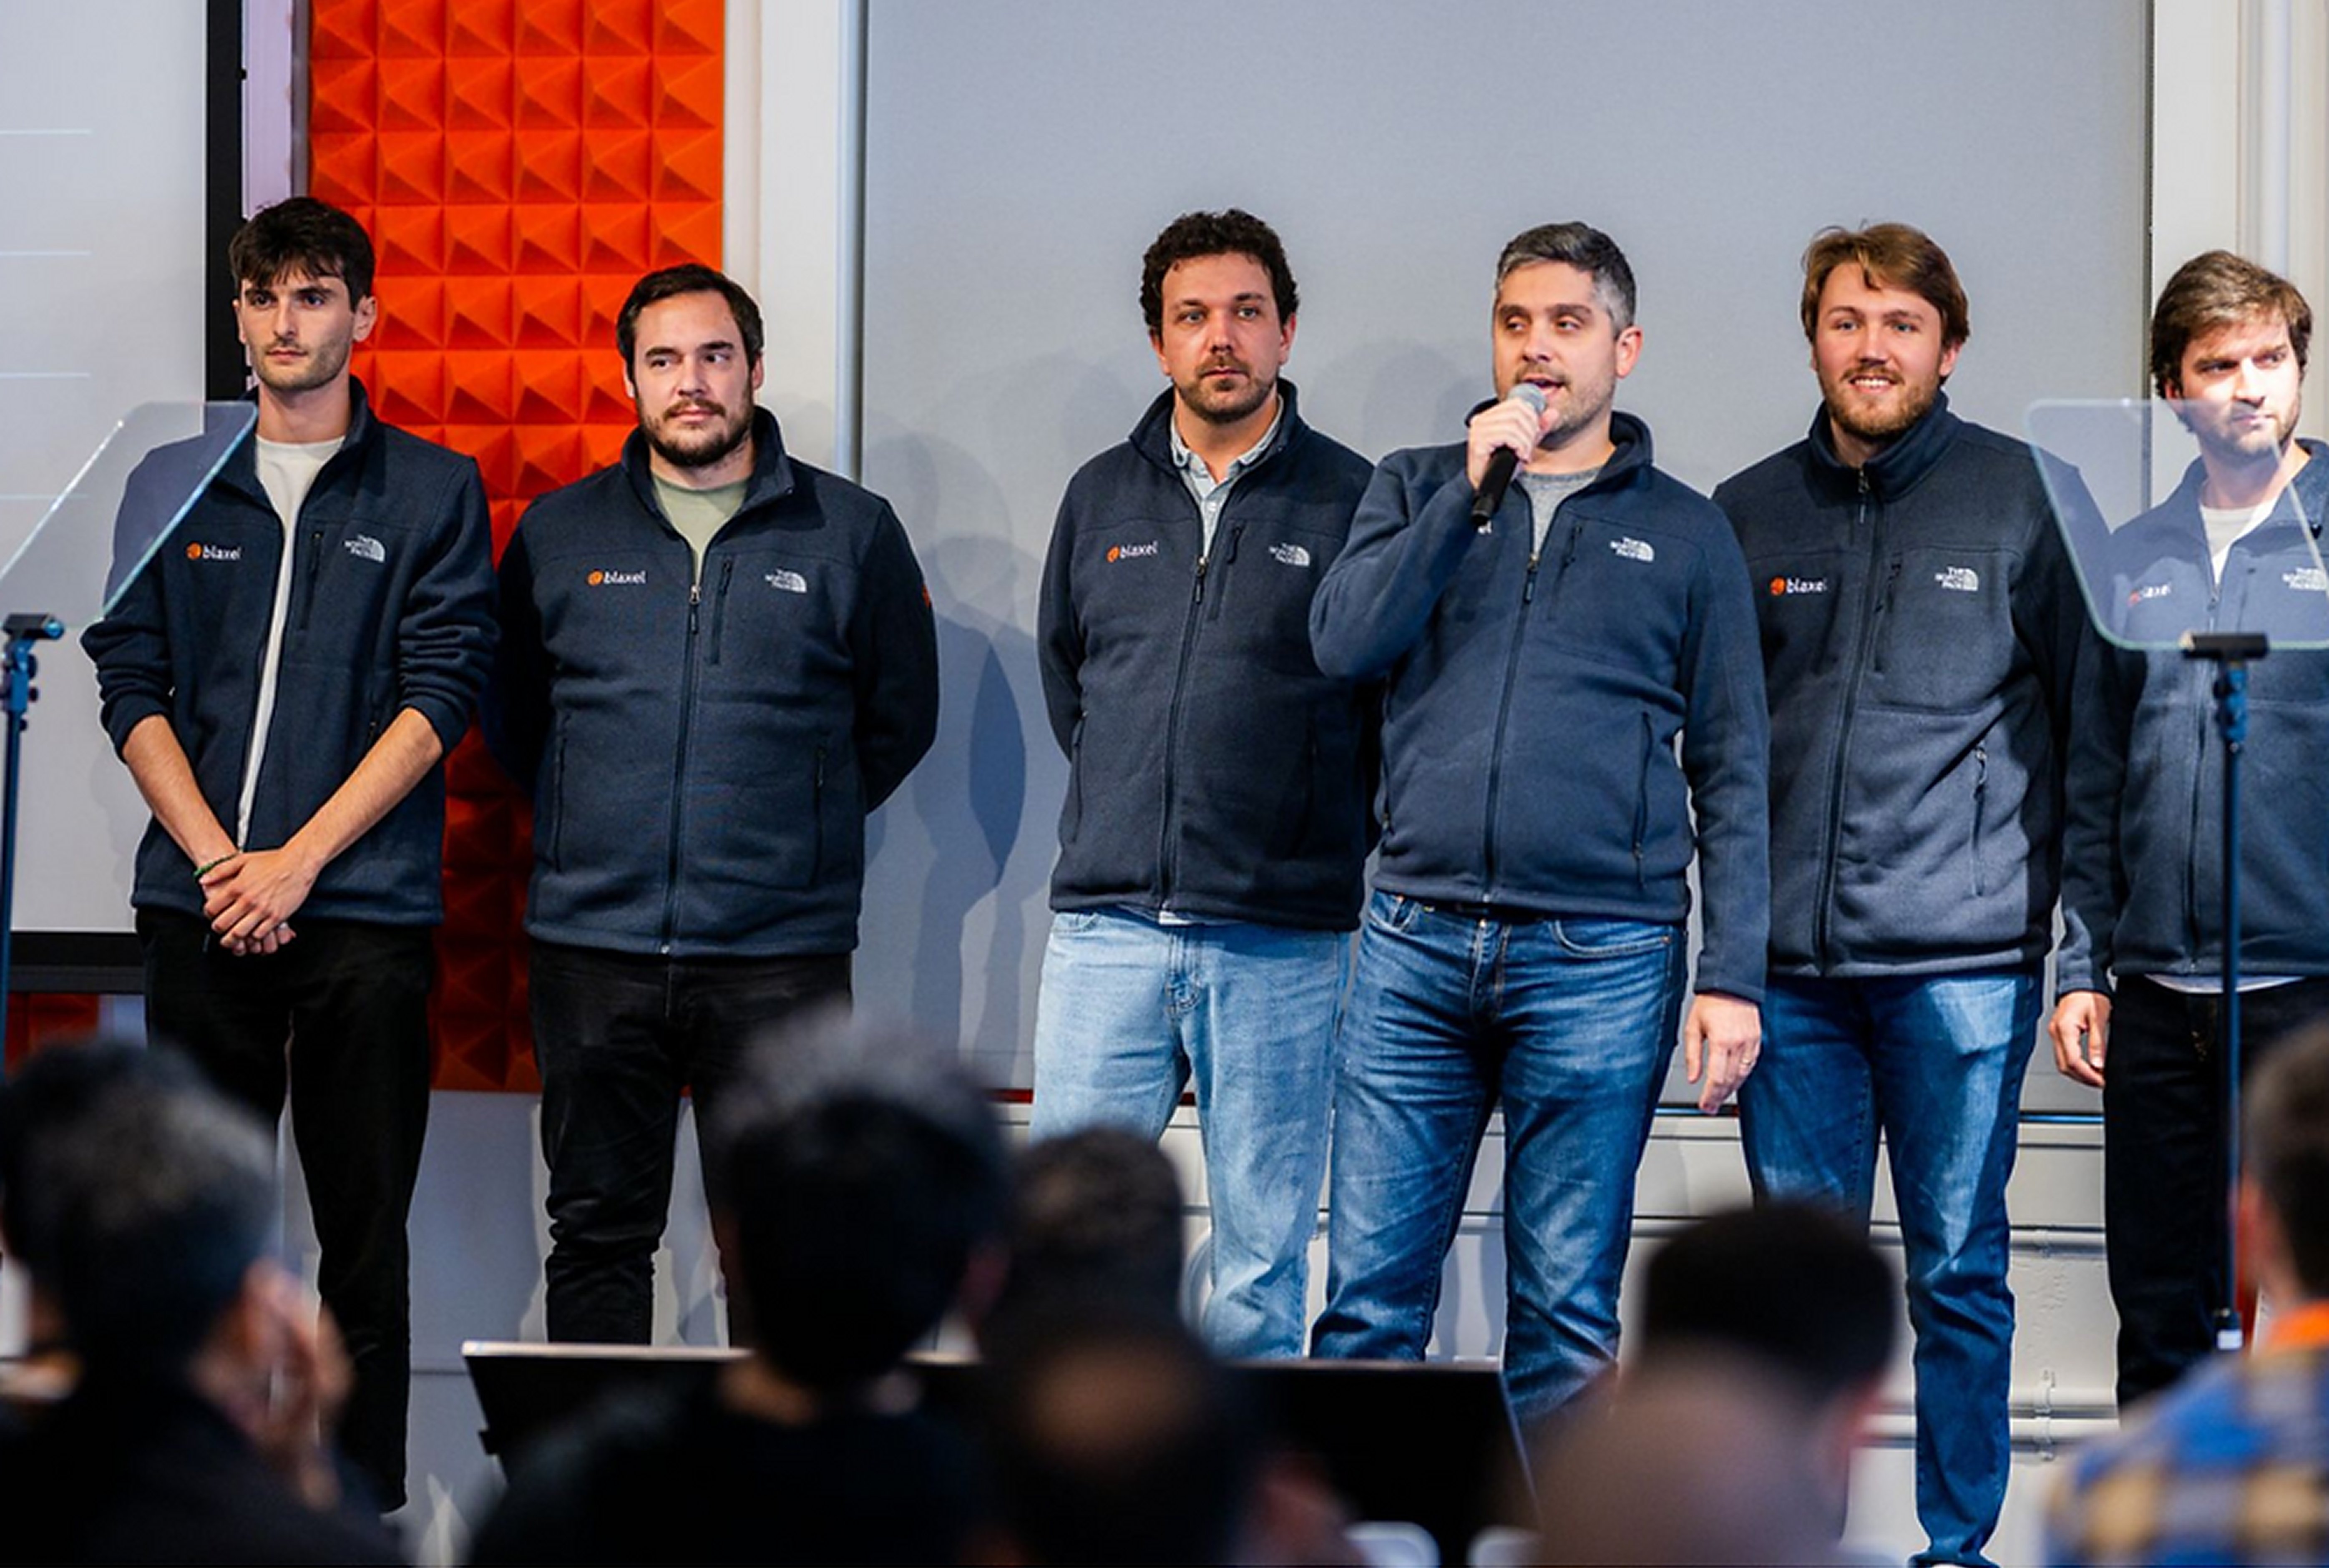
How Blaxel closed enterprise deals without slowing down
Reference case study. This page preserves a real compliance journey as an example of how an expert-supported compliance platform can help a technical company formalize security. Blaxel is not represented as a ZebraByte customer.
The Challenge: Blaxel already had strong technical security foundations, but larger customer opportunities introduced formal requirements around assurance, documentation and governance.
The Approach: The program started with SOC 2, then reused the resulting control structure across ISO 27001, privacy requirements and health-data obligations instead of treating every framework as a separate project.
The Results:
- SOC 2 report issued as the foundation for broader compliance;
- ISO 27001, HIPAA, GDPR and CCPA requirements mapped into one operating model;
- enterprise sales could continue without making compliance a full-time engineering project.
About Blaxel
Blaxel builds infrastructure for AI agents. Its perpetual sandbox environments are designed to retain context and resume execution quickly rather than behaving like disposable short-lived environments.
When a company hosts agent execution, inference, memory and customer workloads on the same infrastructure, security becomes part of the product itself. Customers need confidence not only in performance but also in access controls, incident handling, data protection and the way infrastructure is operated.
Blaxel had treated security seriously from the beginning. The challenge was proving that posture in a way enterprise procurement and security teams could evaluate consistently.
Strong security foundations, but no room for compliance overhead
Blaxel was a small, senior technical team building deep AI infrastructure. Architecture, access control and operational security were already important engineering concerns.
As enterprise opportunities appeared, however, informal good practice was no longer enough. Larger buyers expected:
- security questionnaires with evidence-backed answers;
- documented policies and ownership;
- formal risk management;
- SOC 2 assurance;
- privacy and sector-specific requirements;
- a clear process for security exceptions and remediation.
This is a common inflection point for technical companies. The organization may already be secure in practical terms, but commercial growth requires that security be structured, evidenced and repeatable.
A compliance operating model, not another checklist
The useful pattern in this reference case was to treat software and expert guidance as one operating model.
Rather than asking engineers to maintain a separate universe of compliance spreadsheets, the program could centralize:
- controls and control owners;
- policies and approvals;
- evidence;
- risk assessments;
- vendor reviews;
- findings and remediation;
- framework mappings;
- audit preparation.
Technical questions still require technical judgement, but the coordination and evidence-management burden does not need to sit with every engineer individually.
That same distinction is central to ZebraByte’s model. A company or professional adviser can operate the ZebraByte Cloud platform directly, or ZebraByte Managed Compliance can take responsibility for more of the program when the client wants a hands-off approach.
SOC 2 first, then reuse the foundation
The first formal milestone in this case was SOC 2. Once the core program existed, related frameworks became easier to approach because many controls could be mapped rather than recreated.
For example:
- identity and access controls can support several frameworks;
- risk management can feed both security and privacy obligations;
- vendor management evidence can be reused across assurance programs;
- incident-response processes can satisfy overlapping expectations;
- policy approvals and recurring reviews can be maintained once and mapped many times.
This avoids the common failure mode where SOC 2, ISO 27001, GDPR, HIPAA and other requirements become isolated projects with duplicated evidence and competing owners.
Compliance as enterprise enablement
For a company selling critical infrastructure, formal assurance can remove friction from sales rather than add it.
Once the security program becomes auditable, the company can answer enterprise questions faster, demonstrate how controls operate and give buyers a clearer path through due diligence.
The broader lesson is not that every startup needs every framework immediately. It is that the compliance architecture should be reusable enough that a new framework does not force the team to start from zero.
What another technical company can take from this case
A similar company can use the following sequence:
- Start with the commercial or regulatory requirement that is actually blocking growth. Do not implement frameworks simply to accumulate badges.
- Inventory the controls already operating in production. Good engineering should become the starting point for compliance.
- Formalize the missing governance. Define owners, policies, evidence and recurring reviews.
- Build one control library. Map multiple frameworks to that library instead of maintaining separate programs.
- Keep expert judgement available. Automation can collect and organize evidence, but scope, risk and remediation decisions still need expertise.
- Use the program continuously. Compliance should remain part of operations after the audit is over.
For AI infrastructure in particular, that foundation can become part of the company’s enterprise value proposition: buyers gain evidence that the systems running sensitive workloads are backed by a mature security program.
